Sometimes even the most seasoned cybersecurity professionals need a quick refresher on the foundations everything else is built on. One of the most fundamental concepts in information security is the idea of risk.
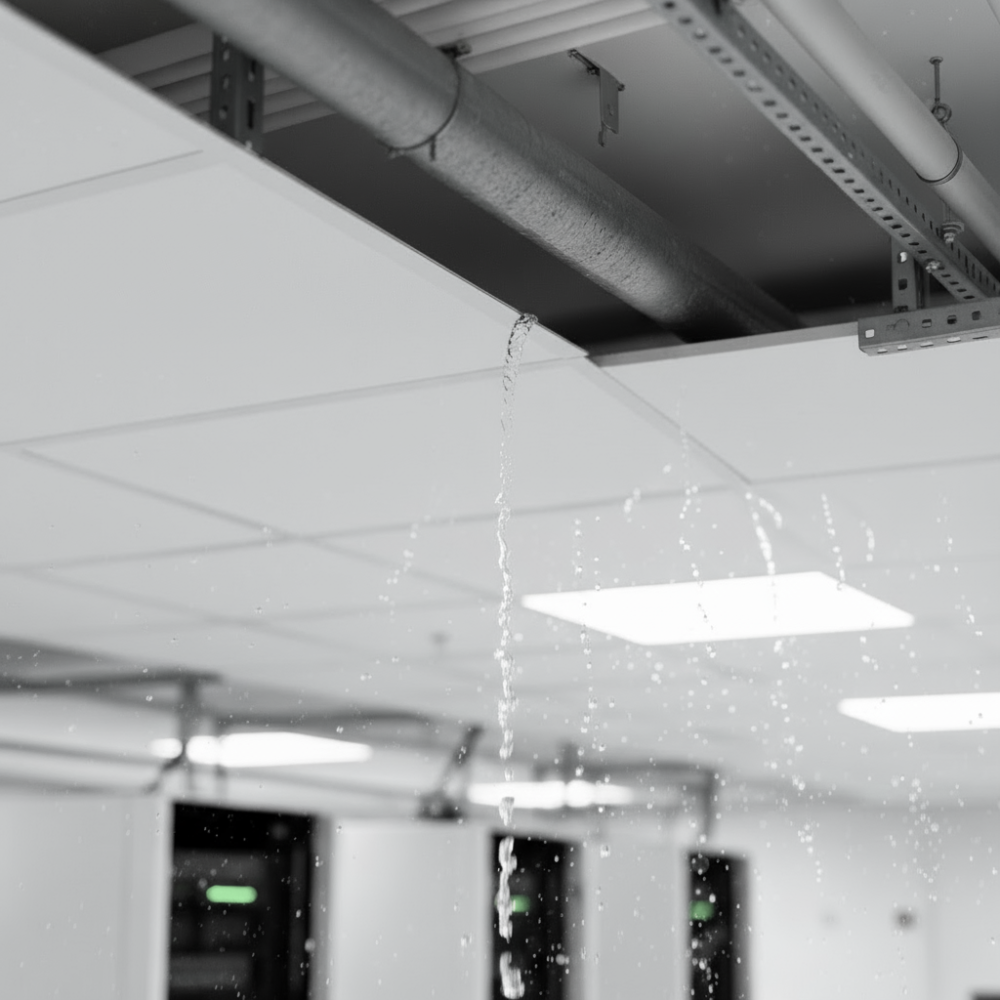
There is an unlimited number of risks an organization could face. A data center can be attacked by a malicious group or destroyed by something as simple as a leaking pipe. The range of possibilities is infinite.
In simple terms, risk is the potential for loss or damage either through a cyberattack, a system failure, or even a natural disaster.
An organization has limited resources (time, money, and people) to address every possible risk. That's why managing risk is all about prioritizing which risks to address, and which ones to accept.
To better understand risk in cybersecurity, we need to understand two other important concepts: threats and vulnerabilities.
A vulnerability is a flaw or weakness in a system that could lead to a loss of confidentiality, integrity, or availability (CIA triad). Vulnerabilities can exist in technology, processes, or people. A software bug that lets an attacker run code remotely is a vulnerability. So is a process that lacks revoking old user accounts, or an employee who has never been trained to spot a phishing email.
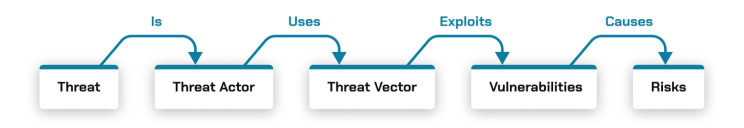
On the other hand, a threat is the potential for a vulnerability to be exploited. We say that a vulnerability is "exploited" when a threat actor uses a threat vector (the method or pathway) to take advantage of the vulnerability.
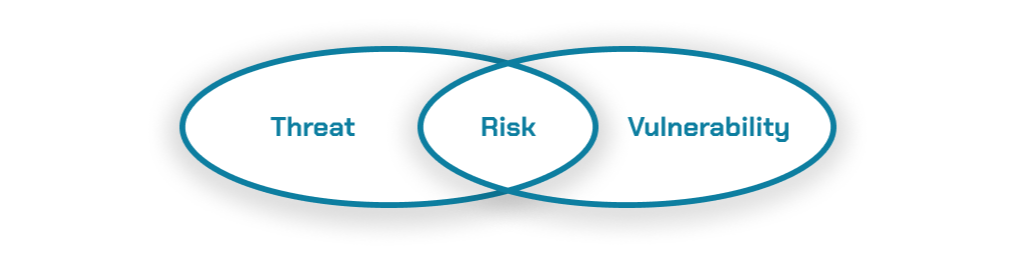
When a vulnerability meets a threat, the result is risk. In professional cybersecurity frameworks, this relationship is captured more formally: for instance, according to ISO, risk is the likelihood and impact of an event that could affect the objectives of an organization (financial, reputation, mission, legal, etc.).
The classic formula says it simply: Risk = Likelihood x Impact. Measuring likelihood and impact is as much an art as it is a science. It requires understanding the business, the culture, the people, and the technology, all at once.
It helps to bring this into concrete terms by looking at two examples: A ransomware attack and a building fire are very different in nature, but both are threats that can interrupt operations and damage an organization (financially, reputationally, or otherwise). Both have probabilities and impacts, and both deserve attention in any cybersecurity risk discussion.
Cybersecurity isn't about eliminating every risk but rather understanding which risks matter the most and managing them accordingly.
Understanding risk is one thing, prioritizing it is another. How do you determine which risks truly matter to your organization?
Originally published in SecDojo Insights on LinkedIn.
View original publication