Build Elite Red Team and Pentest Operators

Advanced offensive security training for penetration testers and red team operators to conduct realistic adversary emulation, master sophisticated TTPs, and battle-test your organization's resilience against advanced threats, with agentic AI adversaries that keep pace with emerging APT tactics.

Offensive Security Aligned to Real Adversaries

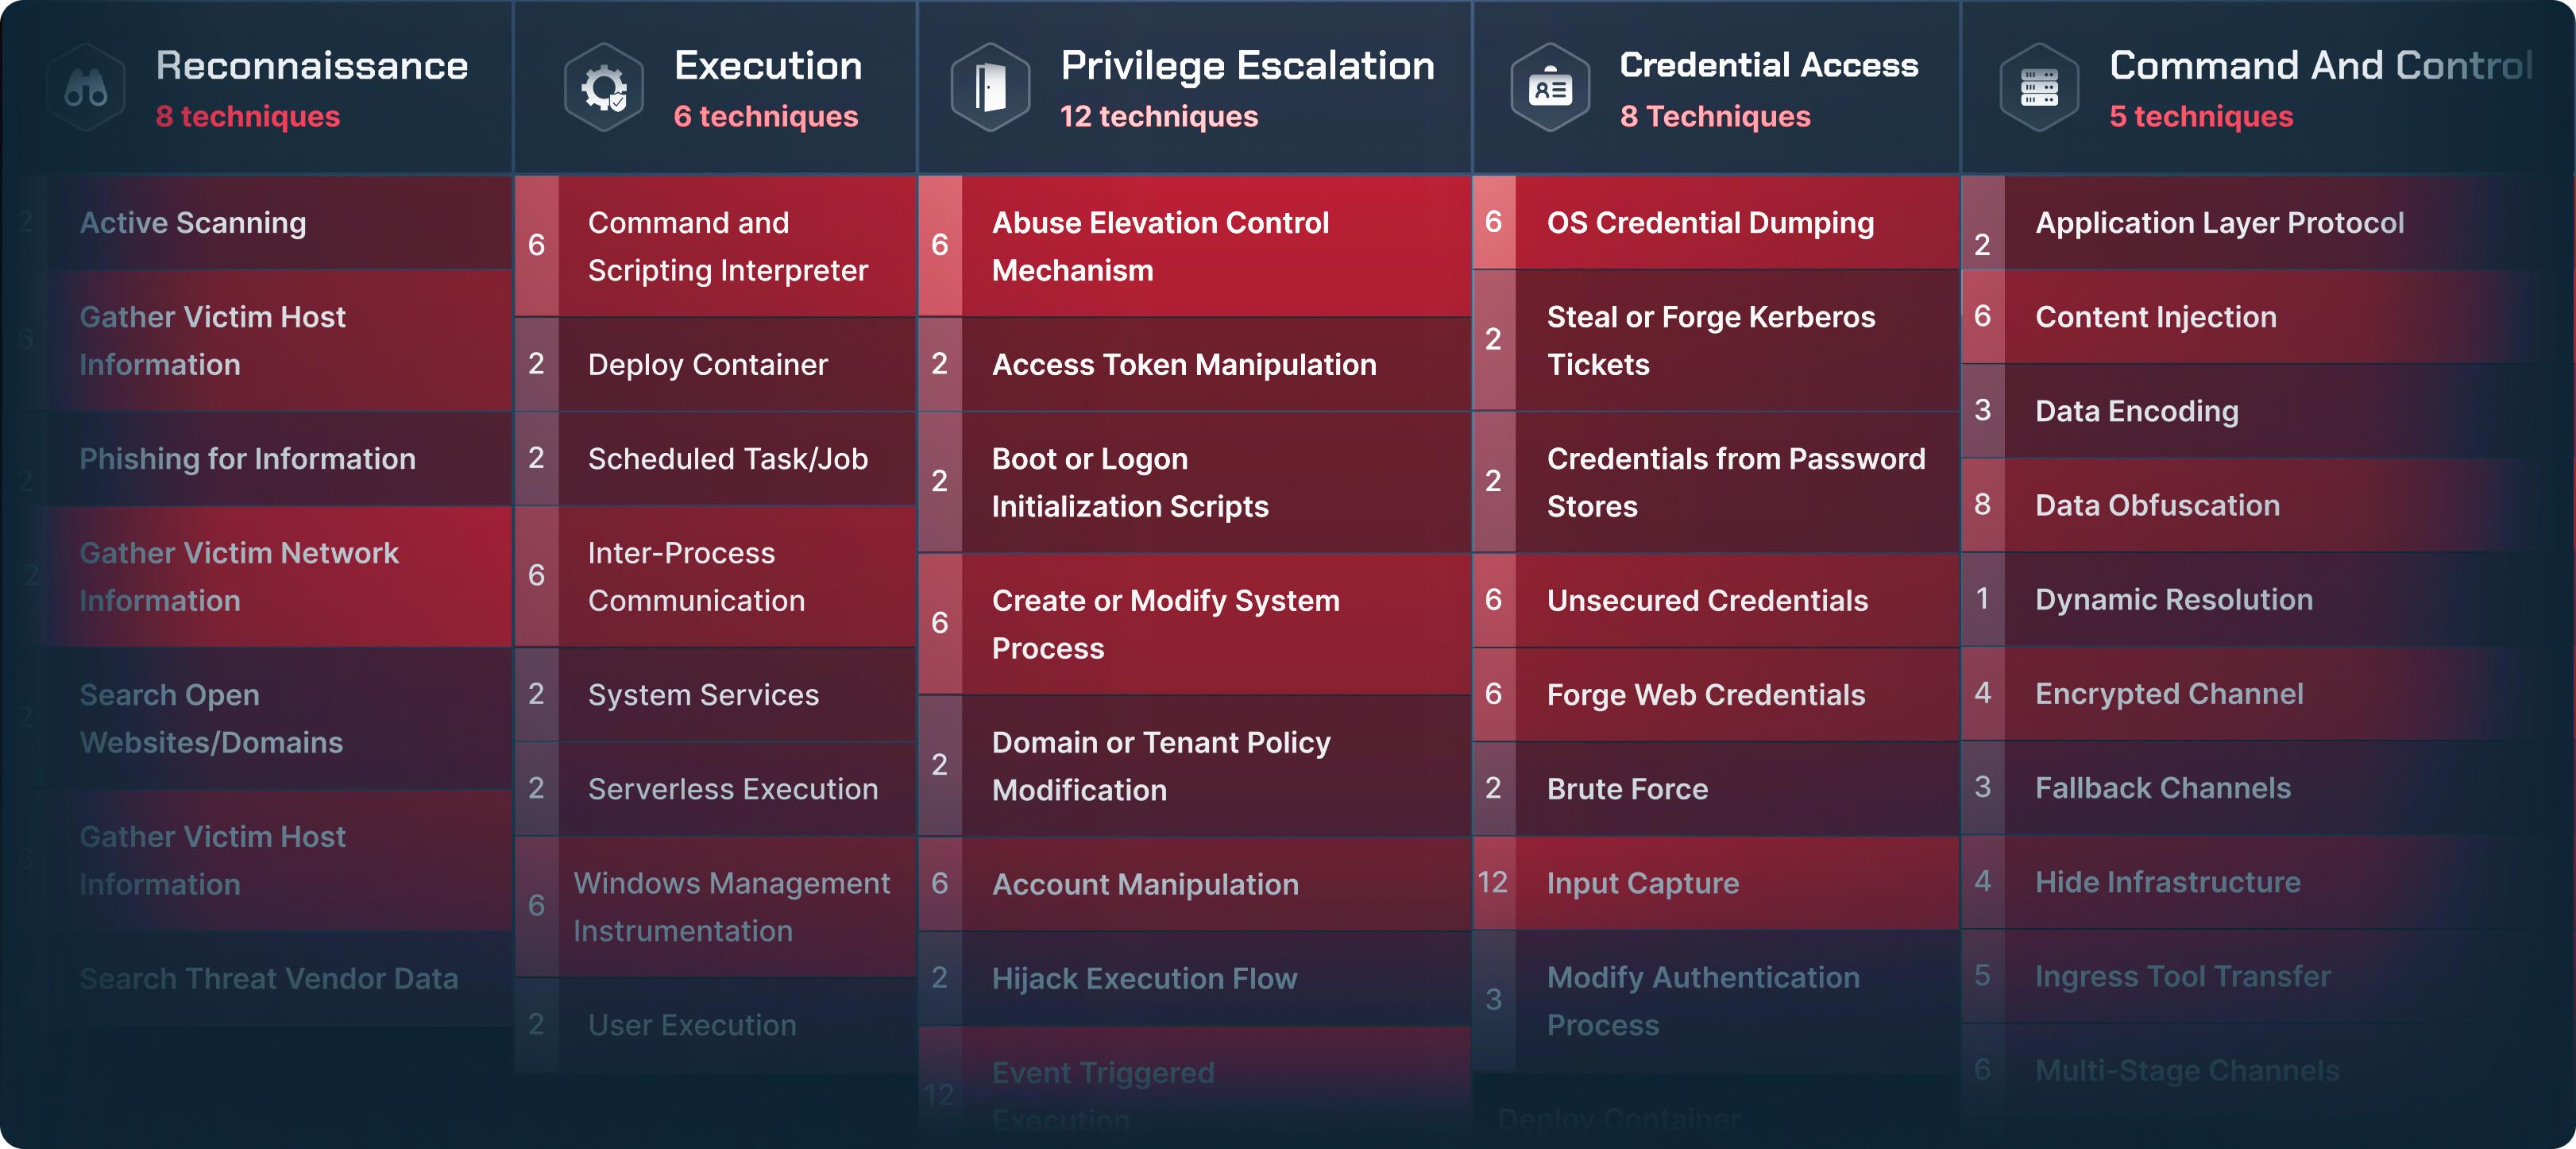
MITRE-mapped cyber ranges enable your red team to conduct realistic adversary emulation through the complete cyber kill chain in IT/OT enterprise environments.

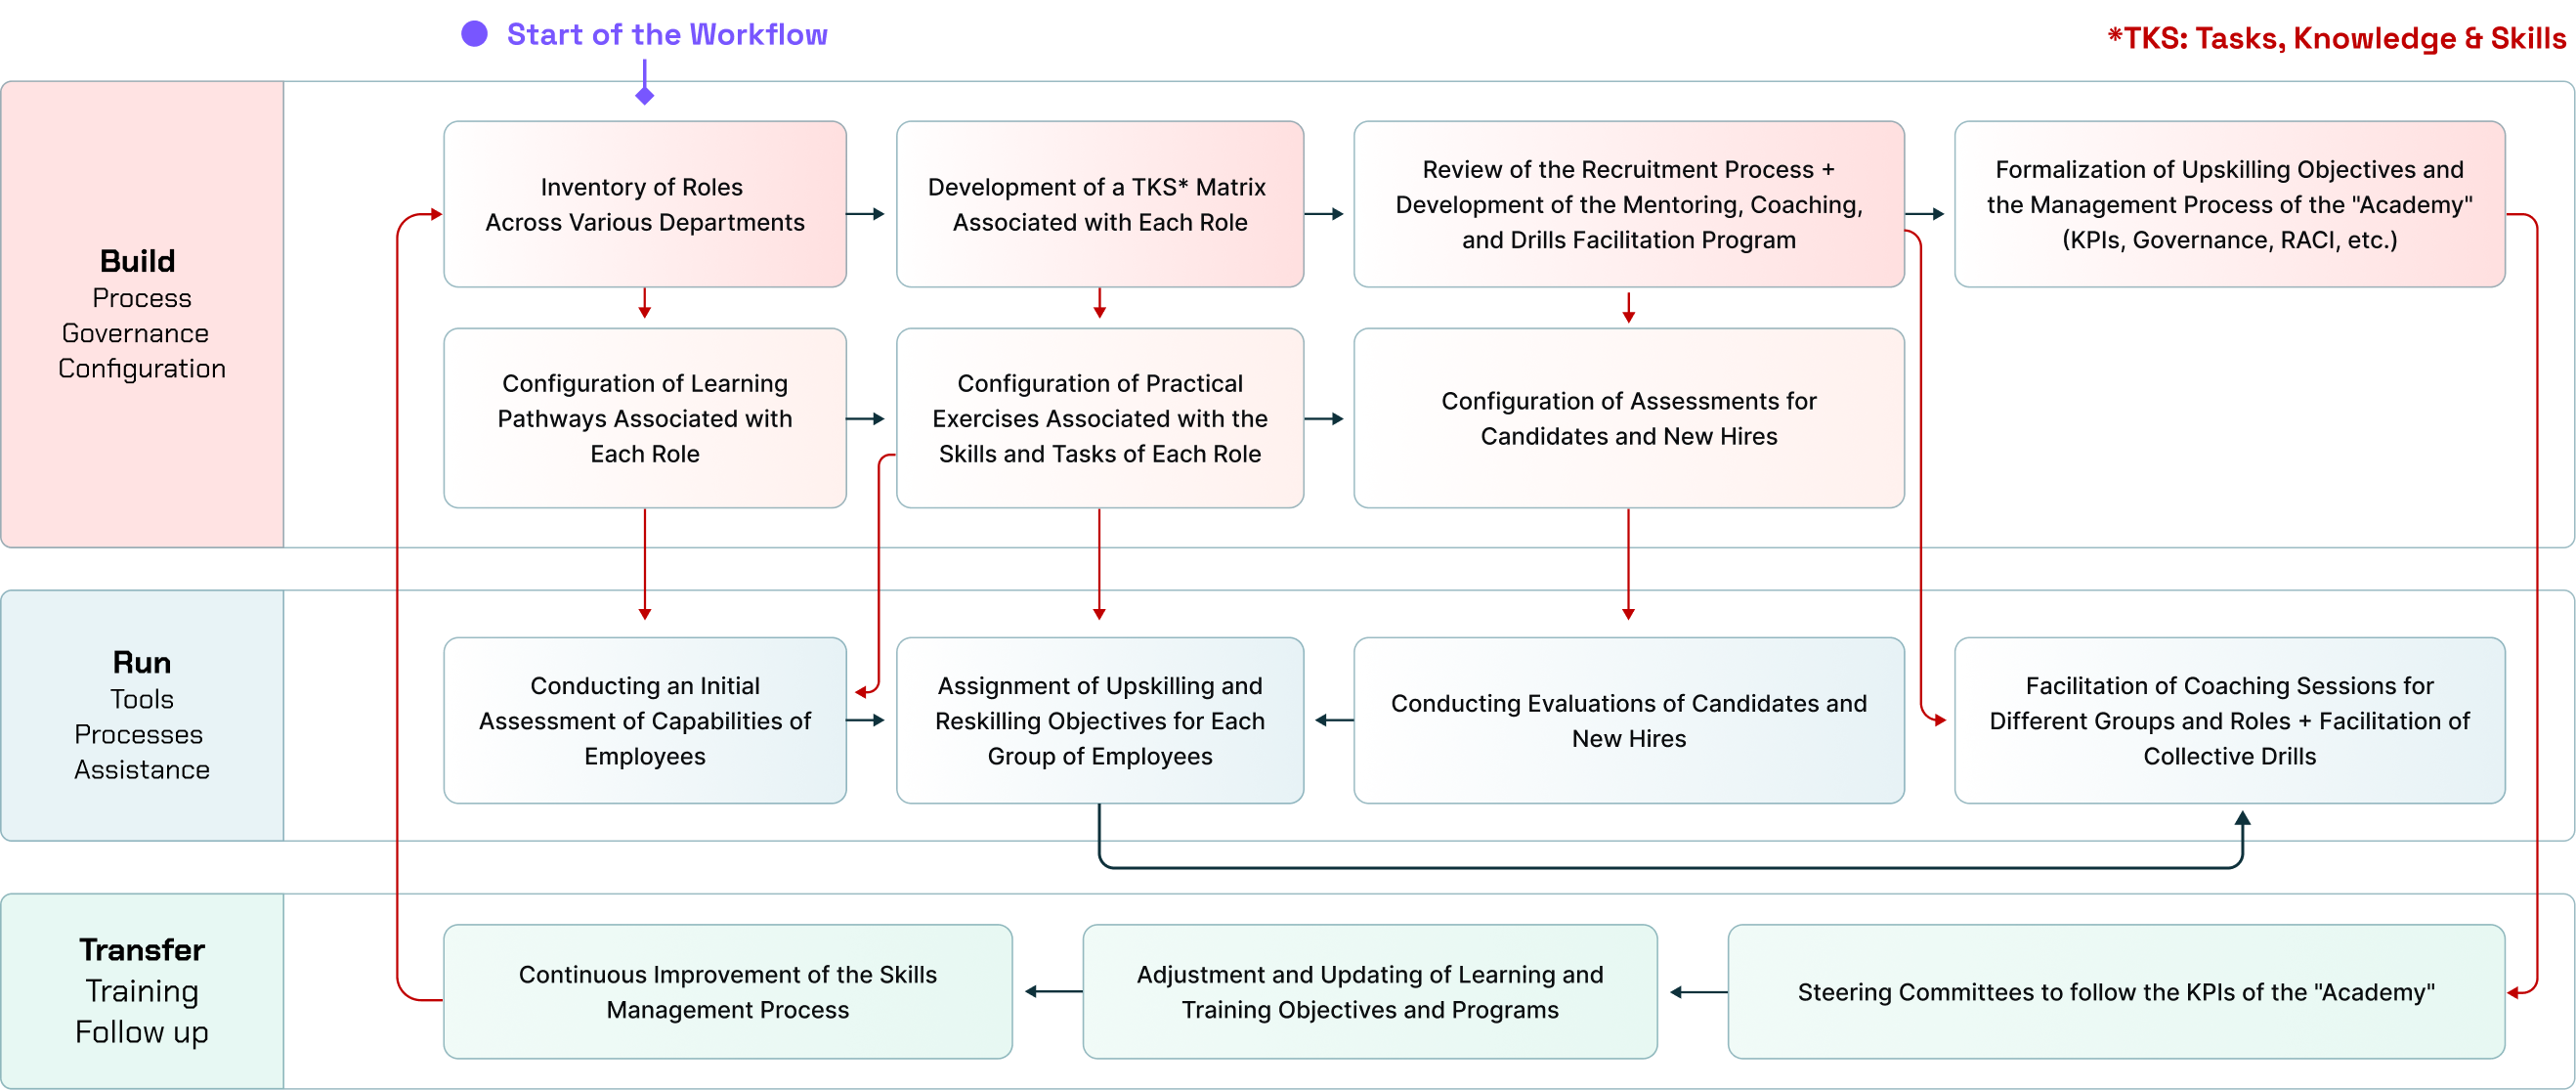
Red Team Attack Lifecycle

Ready to Build Your Red Team?

Download our comprehensive guide on building an elite red team from the ground up, including hiring strategies, training roadmaps, and operational frameworks.

Military-Grade Red Team Training Platform

Build elite red team capabilities through military-grade cyber ranges that train your operators to emulate advanced threat actors, developing the resilience and readiness critical to your organization.

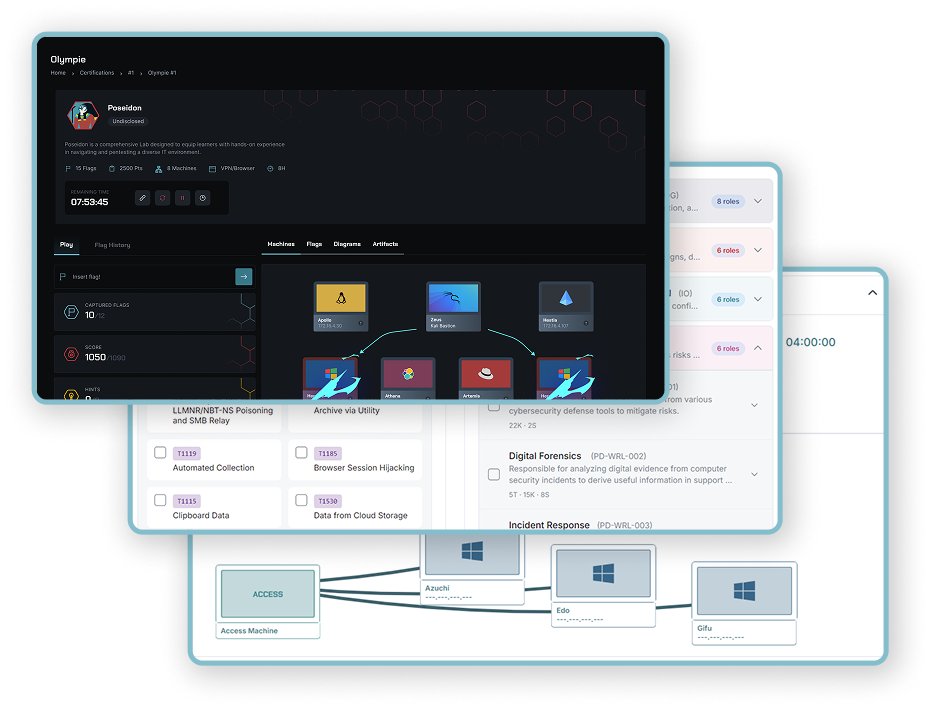
Enterprise Network Environments

Train your operators in enterprise environments featuring Active Directory forests, Cloud and ICS/OT environments, segmented networks, and the latest security solutions.

Complex multi-domain Active Directory forests with realistic trust relationships and misconfigurations
Modern EDR, SIEM, and PAM solutions that operators must evade during engagements
Industry-realistic environments including ICS/OT industrial stacks and Cloud/Hybrid architectures
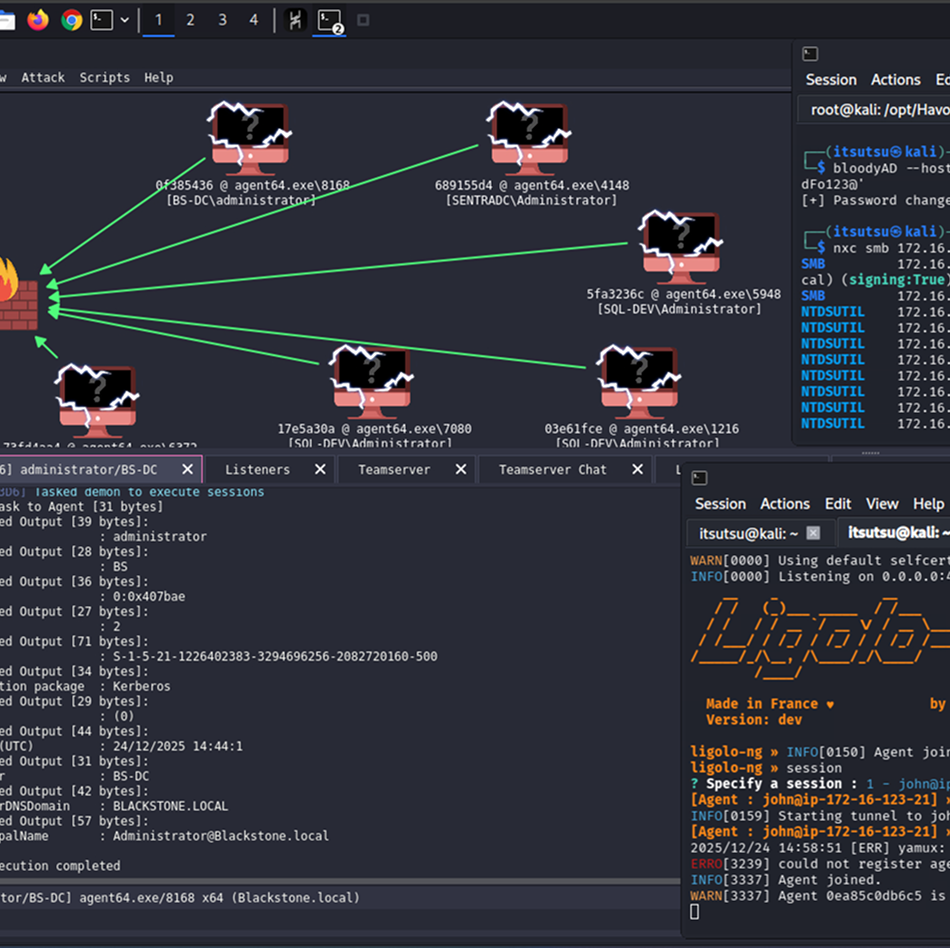
Choose an Ops Box and start BlackStone. Seven machines appear across four networks in a dedicated lab environment.

Advanced Exploitation & Weaponization

Build a world-class offensive security team capable of emulating advanced persistent threats through hands-on training in exploit development, social engineering, and covert command-and-control operations.

Advanced OSINT and social engineering techniques paired with state-of-the-art malware delivery methods
Exploit development and AV/EDR evasion techniques for advanced threat emulation
Red team C2 infrastructure design with OPSEC-focused operational security best practices
Advanced Exploitation & Weaponization

Purple Team Collaboration Exercises

Bridge the gap between offensive and defensive operations through joint exercises that validate detection capabilities, strengthen incident response procedures, and build unified security teams that understand both sides of the battlefield.

Joint red/blue team drills with live real-time attack and defense dynamics
Detection and response validation by testing SOC capabilities and security monitoring effectiveness
Threat intelligence-driven adversary emulation mapped to MITRE ATT&CK frameworks
Prepare a team event with selected labs, then follow a sequence of lab starts, captured flags, and completed challenges in its activity feed.

Build Red Teams from the Ground Up

Structured learning paths for every offensive security role, from penetration testing fundamentals to advanced adversary simulation, based on industry-standard cybersecurity frameworks and our proven methodology

Red Team Training Paths

Extend your assessments to AI applications.

Practise the assessment of LLM features, AI assistants, and the services behind them. Follow the application's trust boundaries, investigate exposed functionality, and demonstrate impact in a dedicated environment.

Explore AI security labs

Trusted by Elite Security Teams Worldwide

  • Eurafric Information
  • KPMG
  • NITDA
  • Yogosha
  • SYSTRA
  • ENGIE
  • OCP
  • AXA
  • MAP
  • DGI
  • FEC
  • Solocal
  • AUSIM
  • TotalEnergies
  • KIABI
  • ECOWAS
  • Crédit Agricole du Maroc
  • DGSSI
  • Orange
  • 1337
  • Cyber Test Systems
  • Marjane
  • Bourse de Casablanca
  • MTNIMA

Energy & Utilities

TotalEnergies

“The platform is extremely intuitive, allowing participants to launch hands-on labs instantly without technical friction. The in-browser lab environment worked flawlessly, ensuring a smooth and efficient experience throughout the cyber exercises…”
Frequently Asked Questions

Questions about practical red team training and adversary emulation.

A red team is an offensive security unit that emulates real-world adversaries using advanced tactics, techniques, and procedures to test your organization's entire security posture, including people, processes, and technology. Unlike traditional penetration testing which focuses on finding vulnerabilities within a defined scope, red teams conduct adversary simulations across your entire attack surface, testing detection capabilities, incident response procedures, and security awareness in realistic, multi-stage attack scenarios.

Building an internal red team provides continuous, realistic validation of your security controls without relying on expensive external consultants. Red teams help you identify gaps in detection capabilities, improve incident response readiness, and validate investments in security tools before a real breach occurs. Organizations with mature red team programs report significantly faster threat detection, reduced breach impact, and improved security team effectiveness, while gaining deep institutional knowledge about their unique threat landscape and defensive blind spots.

SecDojo provides comprehensive, role-based learning paths that take your team from foundational offensive security skills through advanced adversary simulation. Our platform includes structured curricula, realistic enterprise environments, and progressive scenarios that develop the complete skillset needed for effective red team operations, eliminating the need for expensive external training or consultants.

Unlike basic training platforms, SecDojo provides full-scale cyber ranges with enterprise Active Directory forests, modern EDR/SIEM technologies, realistic network segmentation, and Cloud/ICS environments. Your teams train in the same complex environments they'll encounter in production, developing practical skills that directly transfer to real-world engagements.

Our structured learning paths and hands-on cyber ranges dramatically reduce onboarding time. New hires gain practical experience with advanced techniques like exploit development, C2 operations, and evasion tactics in a safe environment, building competency in months instead of years. Progress tracking and skill assessments ensure your team reaches operational readiness faster.

Yes. SecDojo scenarios are based on industry-standard cybersecurity frameworks and can be tailored to your organization's specific environment and threat profile. Purple team exercises allow your red and blue teams to collaborate on validating your actual detection capabilities and security controls.

SecDojo provides detailed analytics and reporting on individual and team performance across all training scenarios. Track skill progression, identify knowledge gaps, and benchmark your team's capabilities against industry standards including MITRE ATT&CK and NIST NICE workforce frameworks. Comprehensive metrics give security leaders visibility into training ROI and readiness levels, with clear alignment to recognized competency frameworks that validate your team's offensive security capabilities.

Teams should have foundational knowledge of networking, operating systems, and basic security concepts. Our modular approach allows you to onboard team members at different skill levels, with progressive scenarios that build from fundamentals to advanced techniques. This enables you to develop talent internally rather than competing for scarce senior red team talent.

Build Enterprise Cyber Resilience at Scale

Discover how SecDojo builds measurable resilience and operational readiness across your entire organization with hands-on cyber-range training.

Comprehensive platform demonstration with mission-critical scenarios
Technical assessment and organizational readiness planning
Training program deployment strategy and integration consulting

Trusted by government, military, finance, and industrial sectors.