Transform Your Software Teams Into Security Champions

Hands-on training for developers, DevOps and AppSec teams, and tech leads that builds security skills at every stage of the software development lifecycle, with AI-adaptive learning paths matched to each developer's tech stack and skill gaps.

Security at the Speed of Development

AppSec shouldn't slow development down. SecDojo accelerates both by training development teams to write secure code naturally through gamified, real-world scenarios.

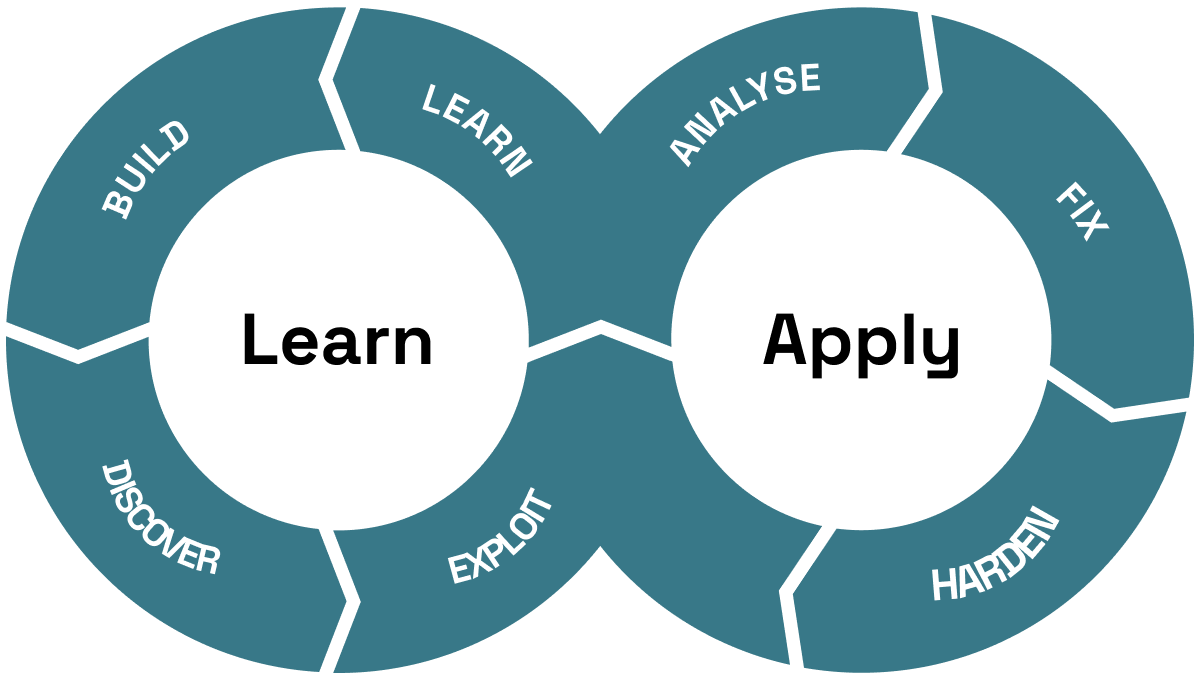
SecDojo Continuous Security Training Loop

Continuous Learning

Build security skills without breaking momentum

Hands-On Practice

Real vulnerabilities, real exploitation, real fixes

Measurable Growth

Demonstrate security maturity to stakeholders

Secure coding in practice

Give developers the skills to fix what scanners find

A security finding still needs someone who understands how to resolve it. Hands-on practice connects the report to the code, so your team can make informed decisions in everyday development.

Understand the finding
Trace a vulnerability back to the code and the assumptions behind it. Learn why it happens in the languages and frameworks your team uses.
Work through the fix
Practise choosing a safer implementation, then test it. Build the judgement to resolve the issue without breaking the application.
Bring it into code review
Recognise the same patterns in the next pull request. Give developers and security champions a shared language for reviewing and improving code.

A Complete Developer Security Training Platform

Practical, real-world training that builds secure developing capabilities and a strong security culture throughout every stage of development

Development Teams Training Pathways

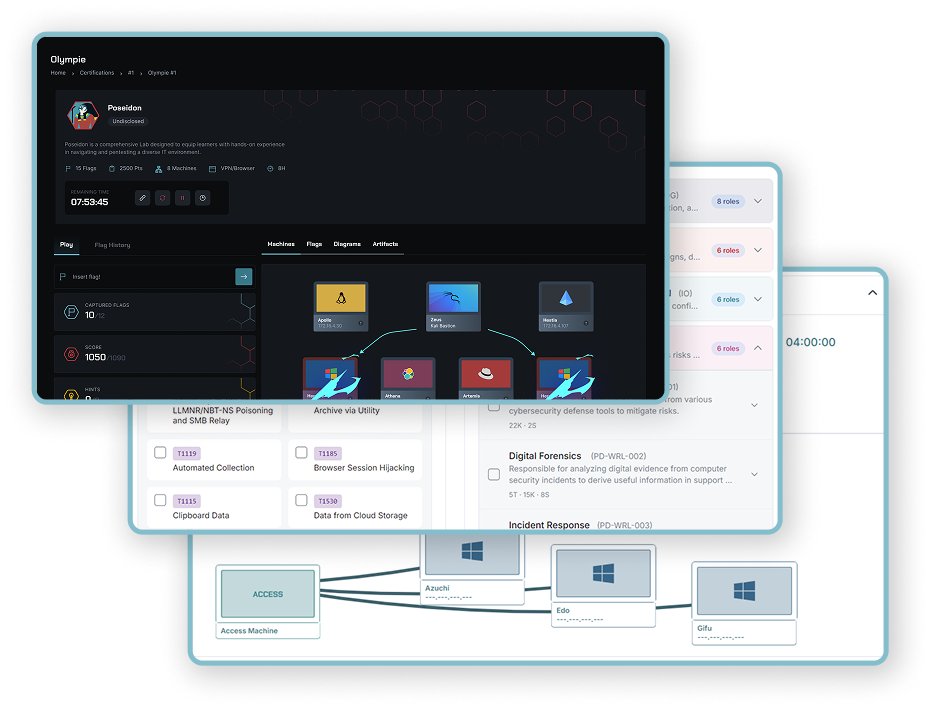
Role-specific pathways for frontend, backend, DevOps, mobile, and security champions with hands-on exercises matched to their tech stacks and the vulnerabilities they face.

Developers prove and improve security skills through hands-on labs
Security embedded throughout the SDLC to shift left and catch issues early
Pathways customized with intelligent automation to match your organization's unique tech stack, threats, and security priorities
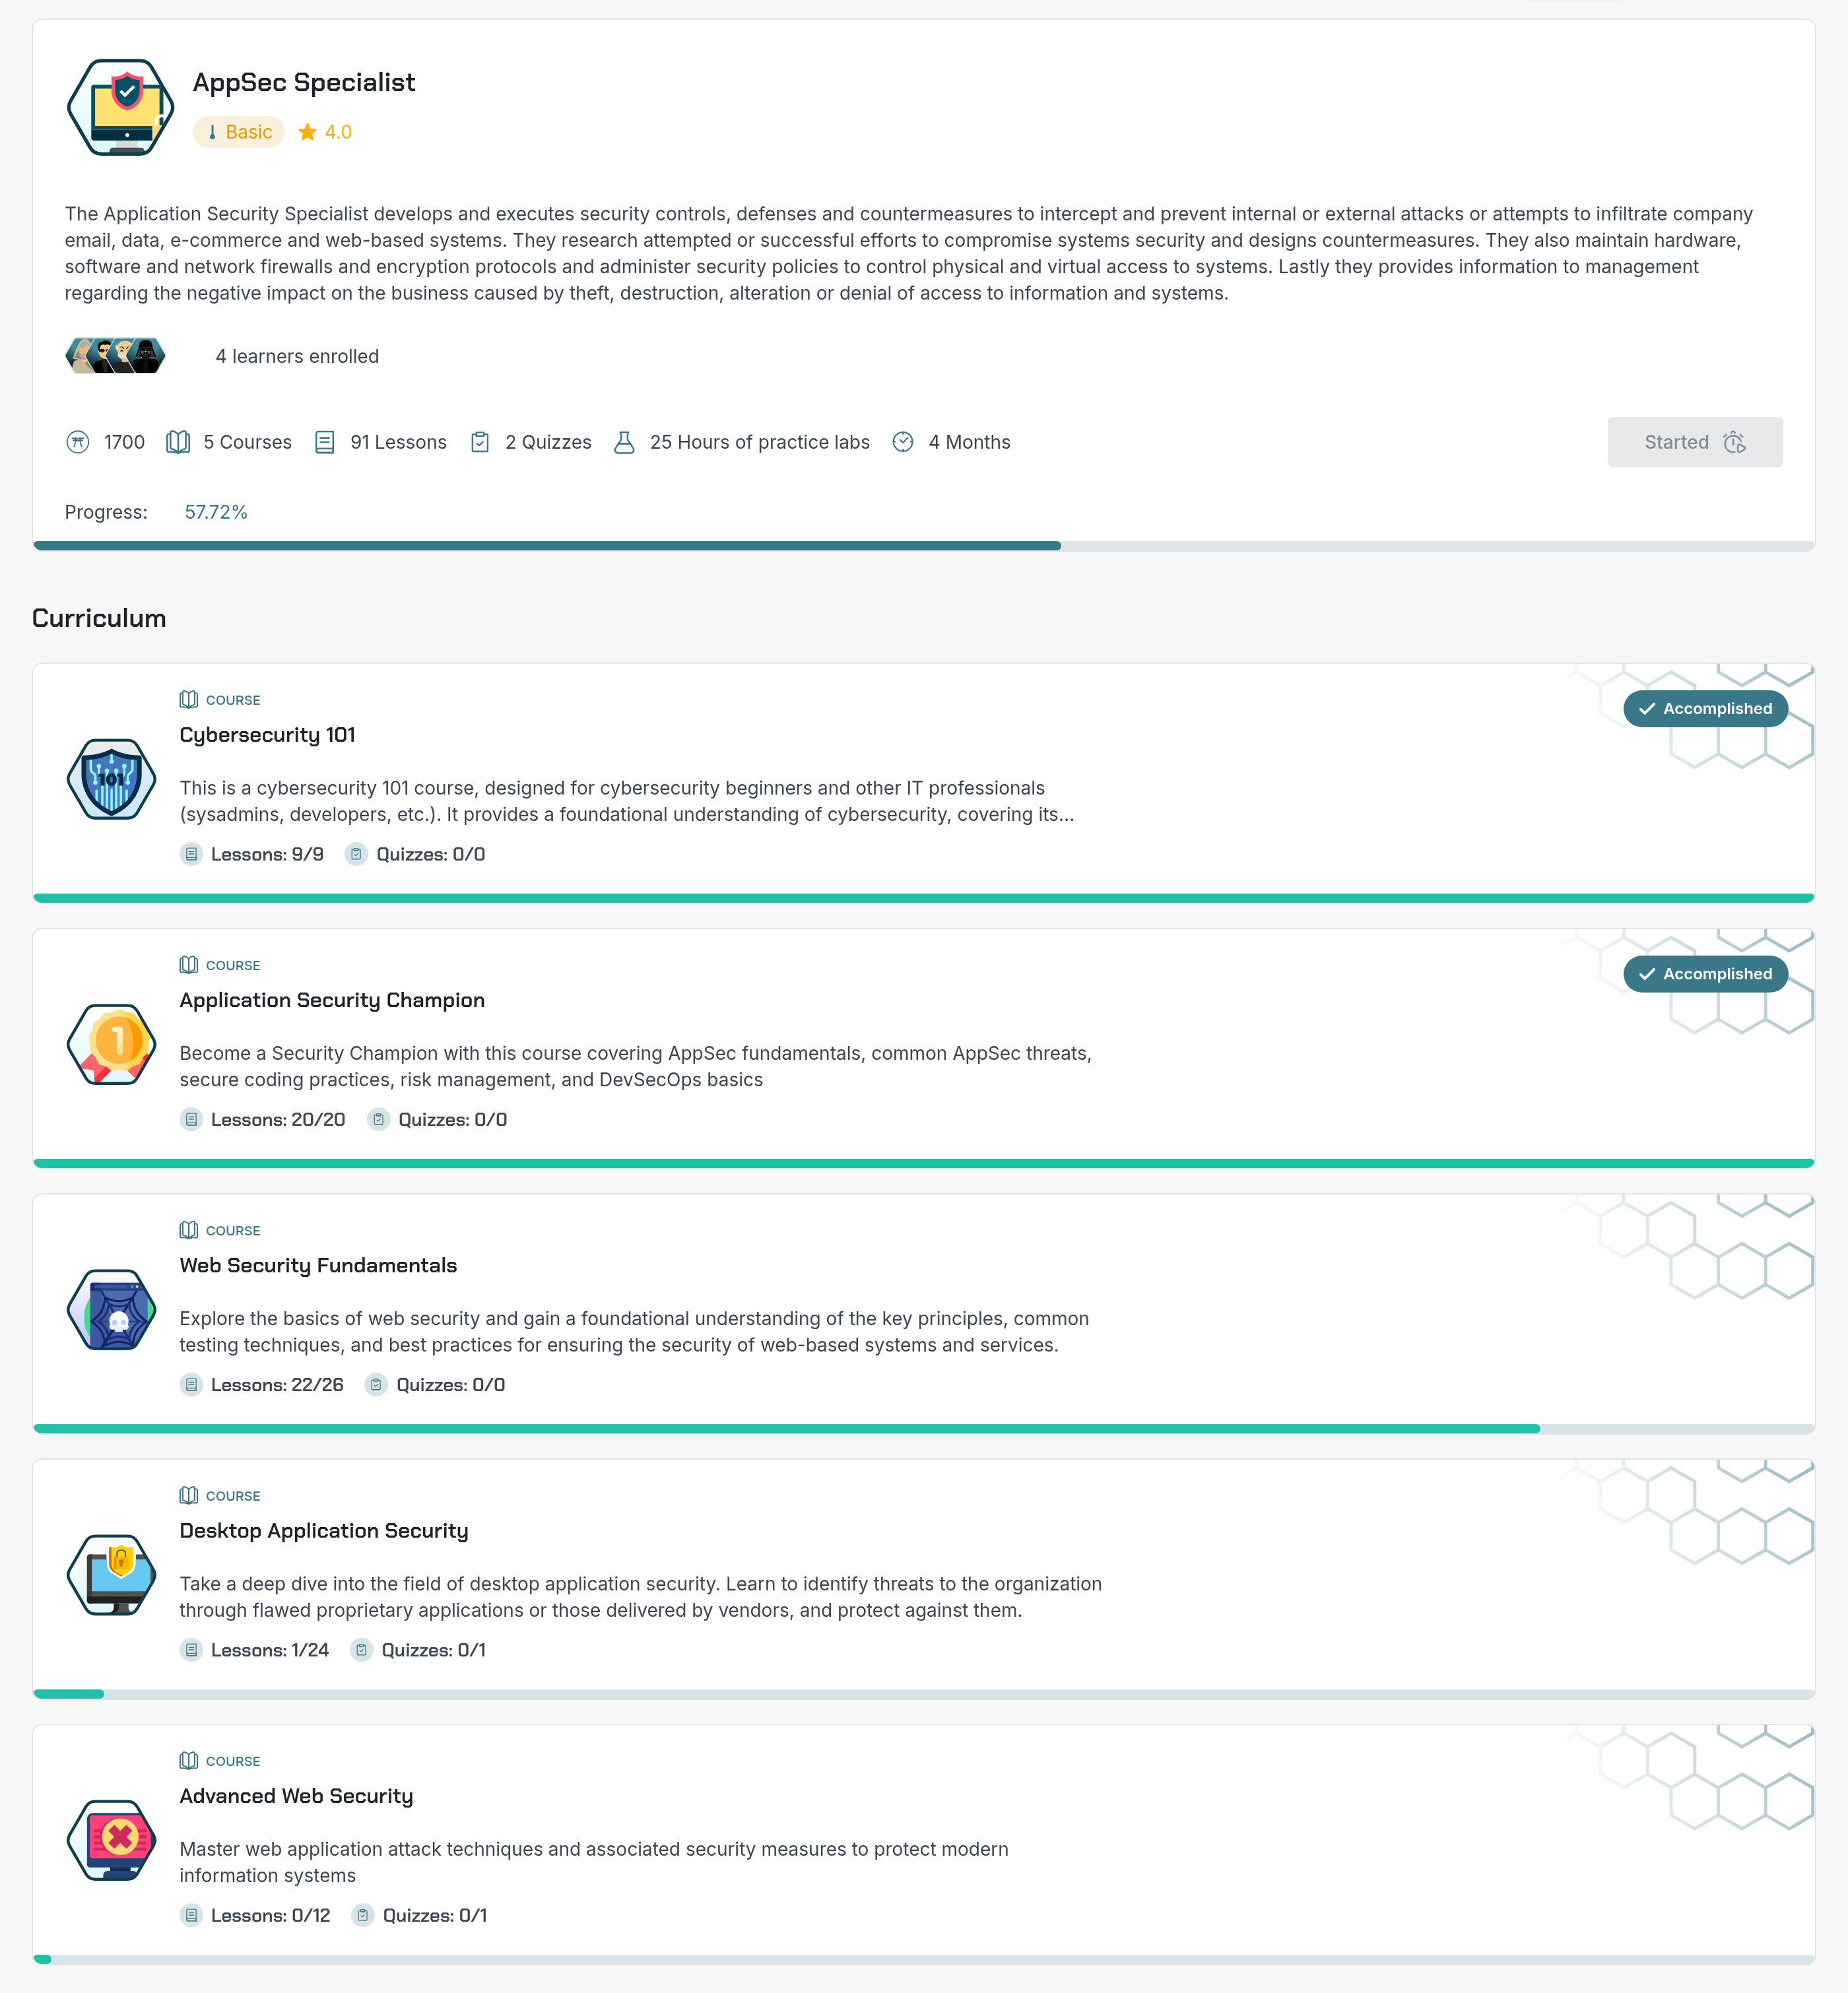
Follow the AppSec Specialist pathway from Cybersecurity 101 to advanced web security, then open Application Security Champion.

Hands-On Secure Code Training

Progressive and role-based learning with hands-on coding and video lessons across multiple languages, technologies and frameworks. Easily assign content against your most pressing threats like the CWE Top 25 and OWASP Top 10.

Multi-language support: Java, PHP, .NET, Python, Node.js, Go, Ruby, and more
DevSecOps and cloud security training for containers, Kubernetes, and CI/CD pipelines
Hands-on learning paths that build practical, real-world secure coding skills
Hands-On Secure Code Training

Build a Security Champion Program

Give your development team a shared foundation in application security. Assign relevant courses, set a training window, and follow each learner's progress before choosing the next challenge.

Start with Application Security Champion and build toward deeper web security practice
Bring selected learning resources together in a team assignment
Use learning progress to guide follow-up and the next stage of training
Select application security courses, add the development team, and prepare one shared training assignment.

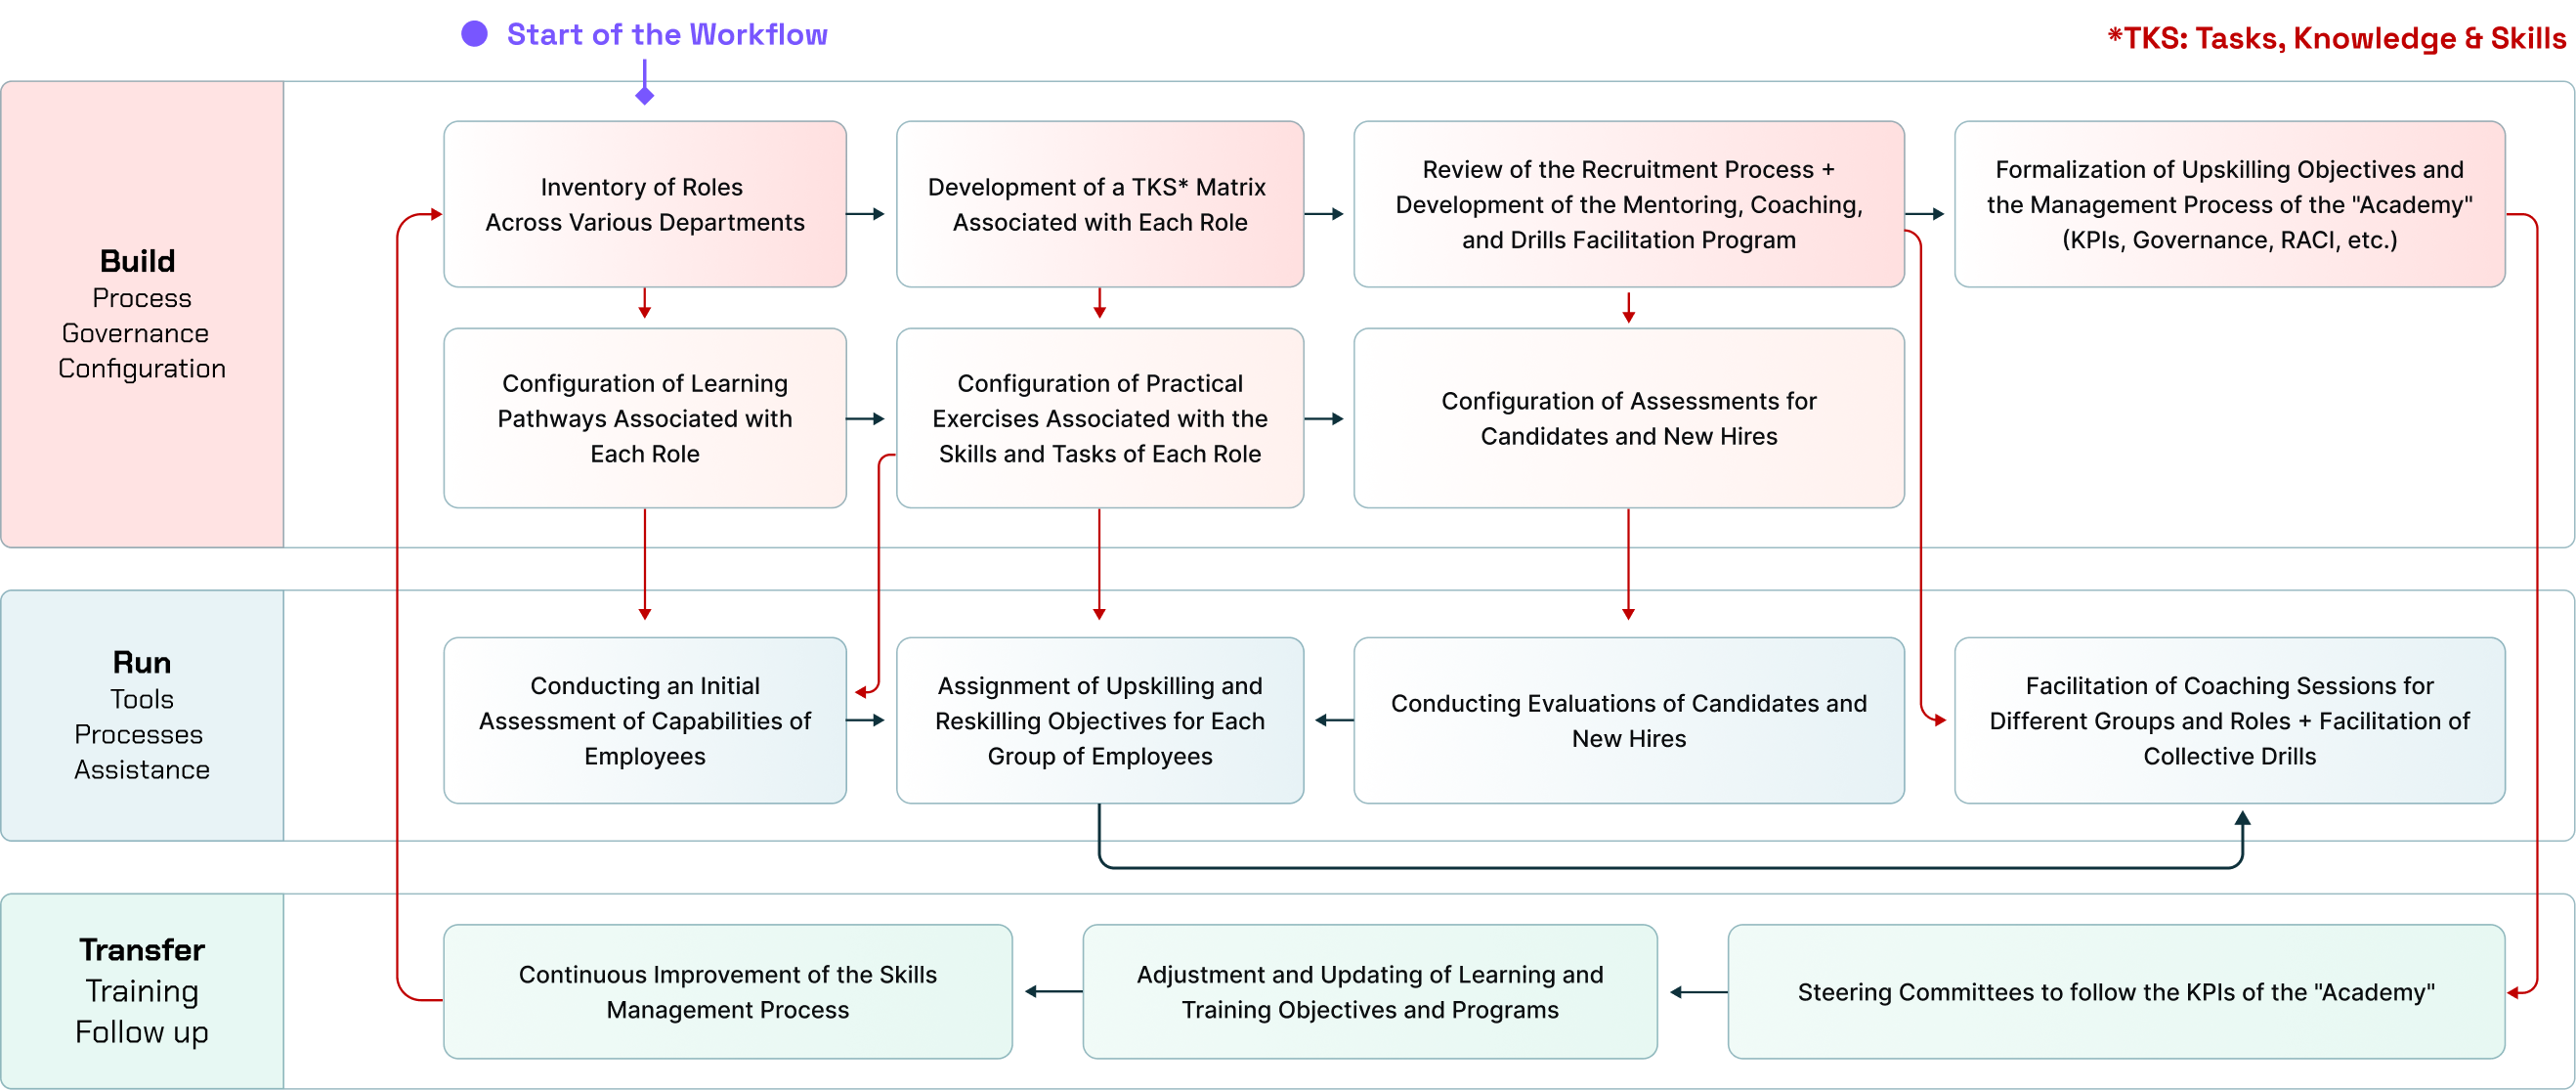
Build and Run Your Security Academy

We combine our expertise with powerful technology to help you build and run a complete upskilling/reskilling program from skills assessment to continuous learning

Role-Specific Training Paths

Build security into AI-enabled applications.

Help developers and AppSec teams understand how AI features change an application's attack surface. Use hands-on scenarios to examine prompt injection, tool access, and the services that connect applications to models.

Explore AI security labs

Trusted by Leading Teams Worldwide

  • Eurafric Information
  • KPMG
  • NITDA
  • Yogosha
  • SYSTRA
  • ENGIE
  • OCP
  • AXA
  • MAP
  • DGI
  • FEC
  • Solocal
  • AUSIM
  • TotalEnergies
  • KIABI
  • ECOWAS
  • Crédit Agricole du Maroc
  • DGSSI
  • Orange
  • 1337
  • Cyber Test Systems
  • Marjane
  • Bourse de Casablanca
  • MTNIMA

Software Development

Solocal

“The labs are very well designed and offer realistic situations, close to scenarios that could actually happen. The platform is clear and accessible, and lets you progressively cover several aspects of IT security…”

Software Development

Solocal

“Secdojo offered me an enriching learning experience that was perfectly suited to my professional needs. Thanks to its well-structured resources and innovative teaching approach, I was able to significantly strengthen my cybersecurity skills…”

Energy & Utilities

TotalEnergies

“The platform is extremely intuitive, allowing participants to launch hands-on labs instantly without technical friction. The in-browser lab environment worked flawlessly, ensuring a smooth and efficient experience throughout the cyber exercises…”

Frequently Asked Questions

Questions about building security skills across the software development lifecycle.

Secure SDLC (Software Development Lifecycle) is a process that integrates security practices into every phase of software development to identify and mitigate vulnerabilities early in the development process.

Secure SDLC Programs are ideal for developers, DevOps engineers, AppSec teams, and tech leads who want to build security skills and integrate security into their development processes.

SecDojo's Secure SDLC training uses hands-on, gamified exercises and real-world scenarios to teach developers how to identify, exploit, and remediate vulnerabilities in their code. We support multiple languages including Java, PHP, .NET, Python, Node.js, Go, and Ruby, with specialized training for DevSecOps, containers, Kubernetes, and CI/CD pipelines. Teams engage through monthly capture the flag and capture the vulnerability competitions, with leaderboards and achievement recognition to build lasting security culture.

Reduced risk of vulnerabilities in production, accelerated development cycles with security built in, improved overall security posture, enhanced team collaboration, and measurable security maturity that you can demonstrate to stakeholders.

The duration of a Secure SDLC program can vary depending on the specific program and the pace of the team. Our 90-Day Implementation Timeline is designed to help teams establish a strong security foundation, integrate security into their workflows, and scale their security practices over a three-month period.

Yes, our Secure SDLC programs are highly customizable. We work with you to tailor the training to your team's specific roles, tech stack, and security goals. Our AI-powered platform intelligently adapts learning pathways based on your organization's unique threat landscape, technology stack, and skill gaps to ensure that the training is relevant and effective for your team.

Build Enterprise Cyber Resilience at Scale

Discover how SecDojo builds measurable resilience and operational readiness across your entire organization with hands-on cyber-range training.

Comprehensive platform demonstration with mission-critical scenarios
Technical assessment and organizational readiness planning
Training program deployment strategy and integration consulting

Trusted by government, military, finance, and industrial sectors.